Give Aikido the chop.
Combat code issues faster with Semgrep

20-30% fewer false positives
Focus on reachable alerts only
Automatically resolve code issues in minutes


10 repositories
Enough to get started, not enough to get serious.
2 users
Barely enough for a pair of devs.
2 AI autofixes/month
Hit the cap on day one and you're on your own.
Single-file engine only
Scans one file at a time. Misses bugs that span across your codebase.
Fair usage limits apply
This is a fancy way of saying “we decide when you've had enough”.

50 repositories
5x more coverage from day one.
10 contributors
Your whole team can start scanning today.
Unlimited AI autofixes
Fix as much as you want.

Pro engine with cross-file analysis
Traces vulnerabilities across files. Catches what single-file engines miss.
No fair usage limits
No hidden limits. No fine print.
Just 50 repos and 10 contributors, free.

20-30% fewer false positives
Stronger reachability analysis
Built for enterprise-scale
Don’t sign up to Aikido.
We let you track
5x the amount of repos for free.



LOVED BY LEADING ENGINEERING TEAMS
Why settle for less?
Our free plan gives you more.
Don’t hold your developers back with Aikido

Noisy, outdated software
As Aikido is built on one of our outdated OSS engines, developers face 20-30% more false positives.

Impossible to scale
Technical audits reveal their scanner often times out or fails on repositories with as few as 100-300 files.

All breadth, no depth
It spreads investment thin across nine products in its suite, so you’re paying for cheap tools that don’t drive results.
Aikido dabbles in 15 dev tools.
Semgrep masters what matters.
Fewer false positives.
Higher baseline accuracy.
Semgrep reduces false positives by 20% on day one. Then, it learns from triage decisions to continually cut your workload, and offer more accurate findings.
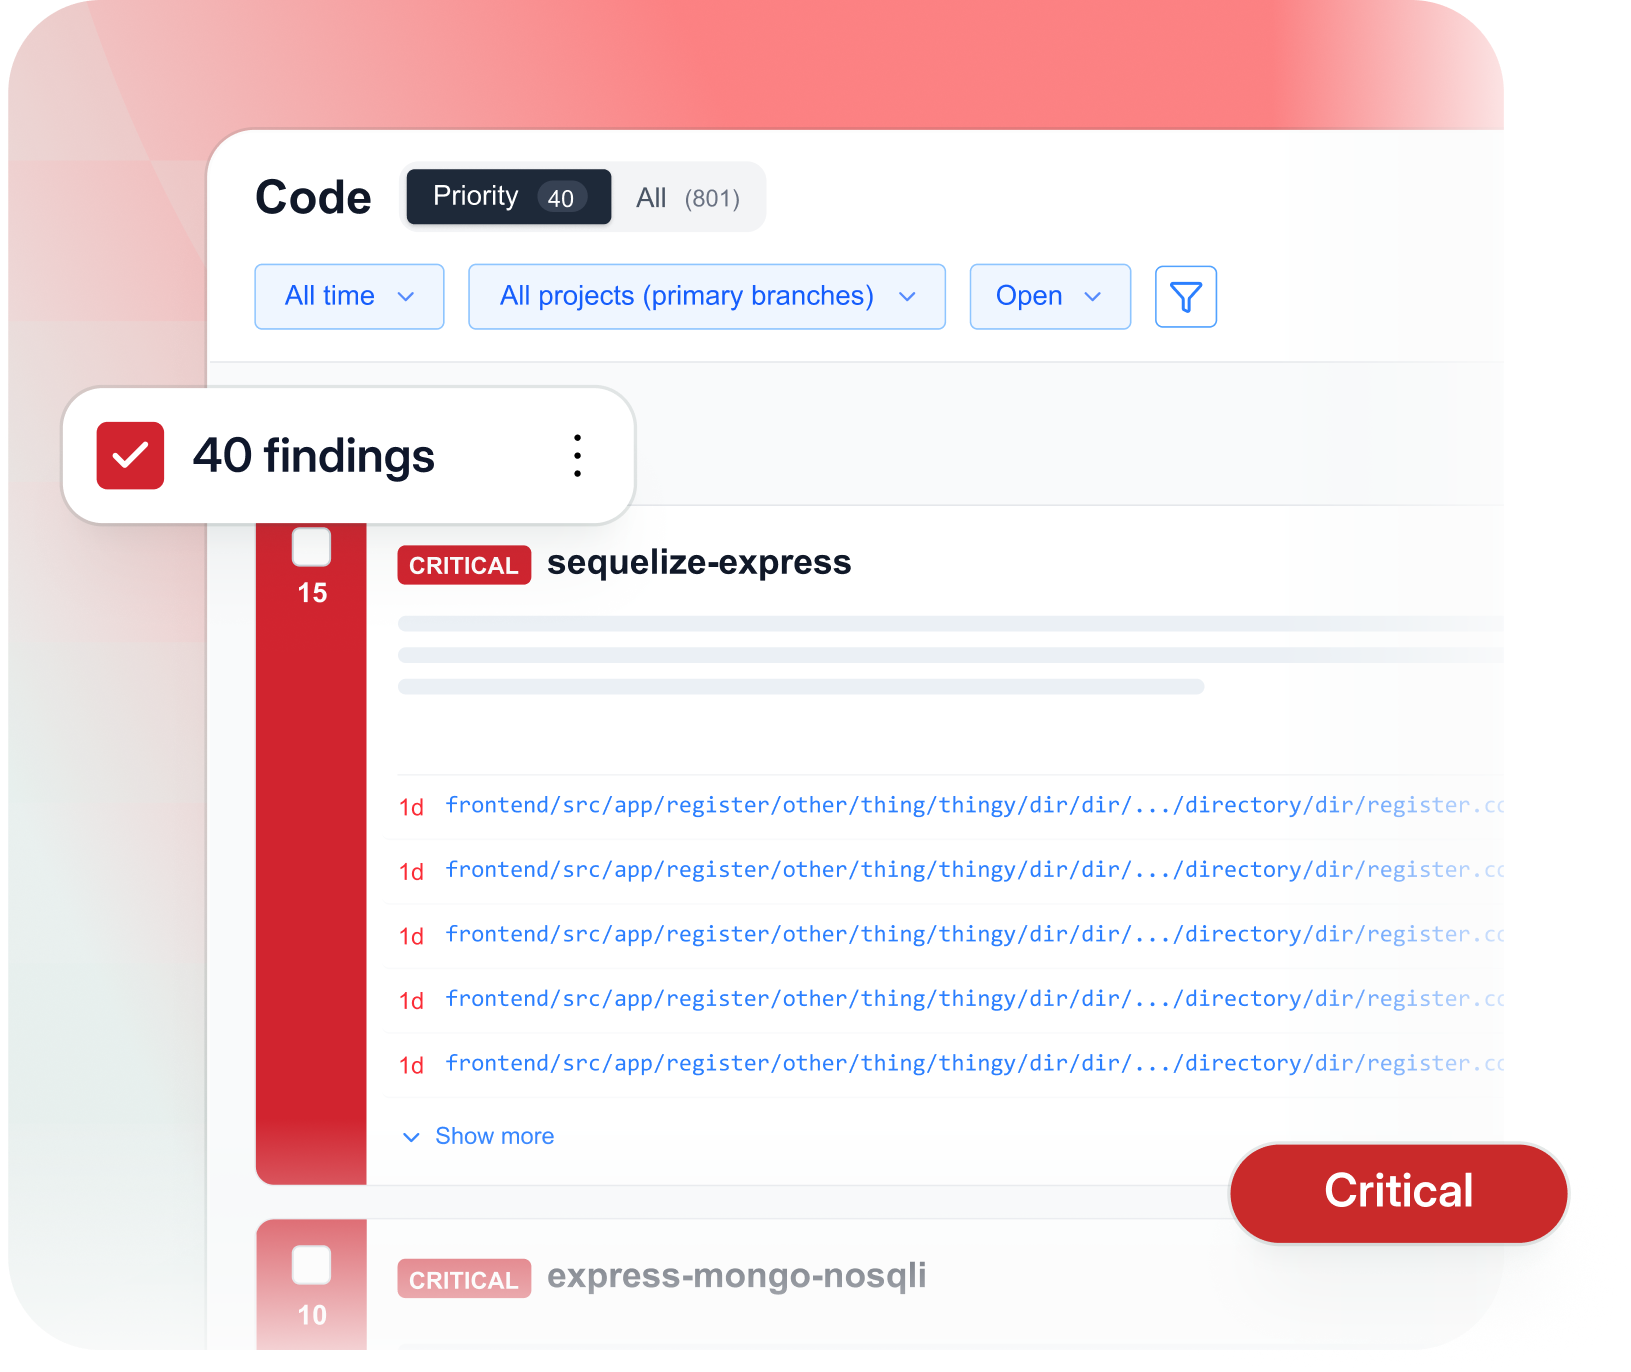
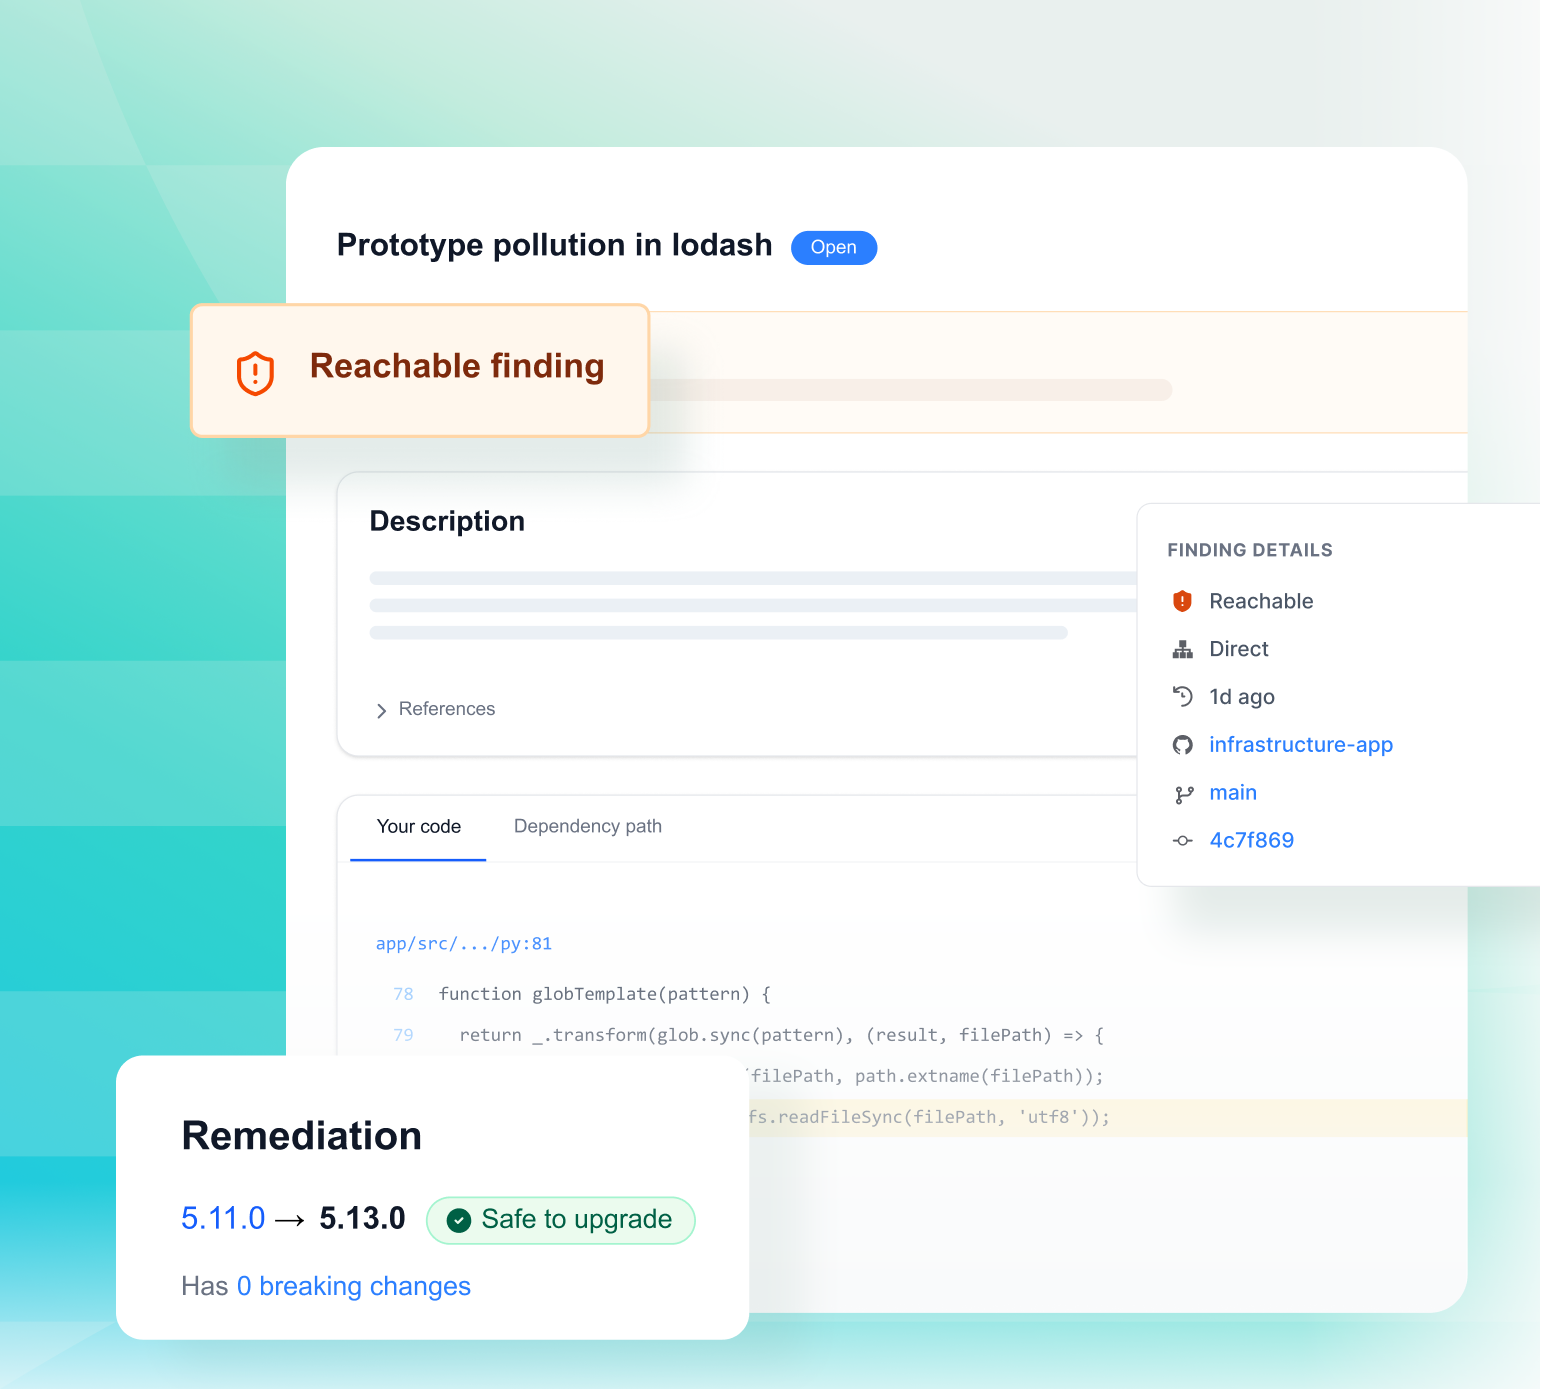
See exactly what you need to focus on
Semgrep presents only reachable findings so developers can focus on the most important issues, and see the exact lines of code with the vulnerability.
Built for enterprise scale
Whereas Aikido is unstable for mature organizations or monorepos, Semgrep is built to handle enterprise scale well. Your team can move fast, without slow scans and failures.
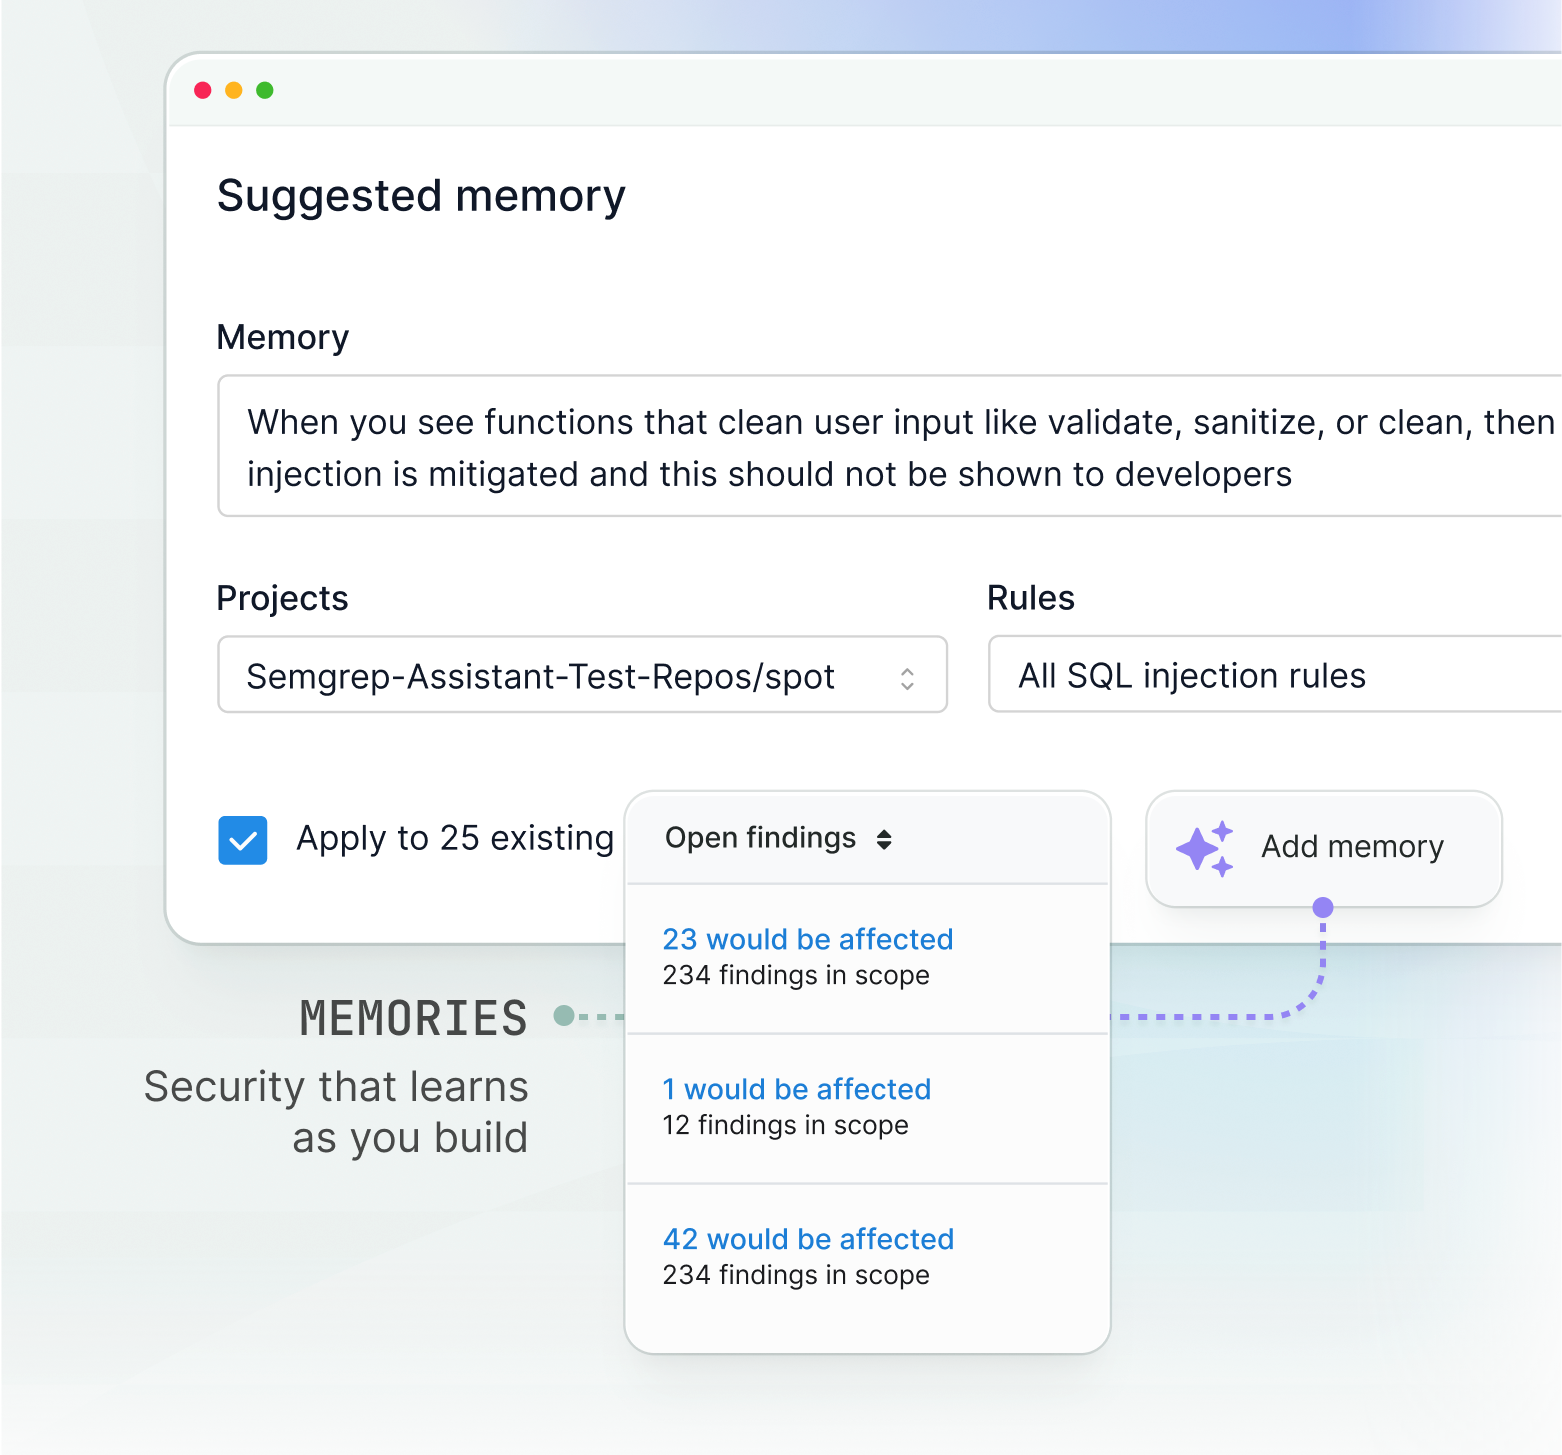
Fewer false positives. Higher baseline accuracy.
Semgrep reduces false positives by 20% on day one. Then, it learns from triage decisions to continually cut your workload, and offer more accurate findings.
See exactly what you need to focus on
Semgrep presents only reachable findings so developers can focus on the most important issues, and see the exact lines of code with the vulnerability.
Find and fix the real issues faster
Semgrep Multimodal delivers tailored remediation guidance directly in pull requests, helping teams save an average of 30 minutes per finding and reduce time to resolution by 22%.
Let’s go head to head


Why security teams
love Semgrep
On average, security engineers cut eight hours of time spent on code triage.
8+ hours saved per week

Semgrep helps you spot-check auto-generated code snippets in minutes, saving hours on research.
30+ minutes saved per finding

After analyzing over 6 million security findings, Semgrep has a 96% agreement rate from users and security researchers.
96% agree rate


We make triage easy
as 1, 2, 3
Semgrep Multimodal uses AI reasoning and codebase context to identify findings that aren't actually exploitable, reducing the number of alerts your team needs to triage.
Automatically filter out false positives
1


Developers receive step-by-step remediation guidance directly in their pull requests, helping them resolve real issues without leaving their workflow.
Get tailored remediation
guidance
2

Semgrep learns from your organization's triage decisions and applies that context to future findings,
reducing repetitive work without requiring custom rules.
Never triage the same issue
twice
3


“It's easy enough to write rules for Semgrep that security and other engineering teams use it to solve complex problems. This flexibility is a huge win, and the library of managed rules means we only have to write our own when we have custom problems.”

Rob Picard
Security Lead
“Figmates get actionable security feedback in their PRs, while rule analytics give the security team feedback on the effectiveness of our rules. The simple syntax lets us extend Semgrep to catch new patterns, going from idea to live in an hour.”

Dev Ahkawe
Head of Security, Figma
“Semgrep makes it so that developers can focus on the issues they need to focus on rather than the ones they don’t.”

Devyani Vij
Senior Application Security Engineer
“Semgrep helped Sola Security scale high-signal security checks in PRs, so developers ship faster with confidence, and security keeps pace without adding friction.”

Yoni Weintrob
Chief Information Security Officer, Sola Security
“It's easy enough to write rules for Semgrep that security and other engineering teams use it to solve complex problems. This flexibility is a huge win, and the library of managed rules means we only have to write our own when we have custom problems.”
Rob Picard
Security Lead
“Figmates get actionable security feedback in their PRs, while rule analytics give the security team feedback on the effectiveness of our rules. The simple syntax lets us extend Semgrep to catch new patterns, going from idea to live in an hour.”
Dev Ahkawe
Head of Security, Figma
“Semgrep makes it so that developers can focus on the issues they need to focus on rather than the ones they don’t.”
Devyani Vij
Senior Application Security Engineer
“Semgrep helped Sola Security scale high-signal security checks in PRs, so developers ship faster with confidence, and security keeps pace without adding friction.”
Yoni Weintrob
Chief Information Security Officer, Sola SecurityDon’t just take our word for it
Frequently Asked
Questions

Aikido is an all-in-one bundle of security tools that incorporates Opengrep (a fork of Semgrep OSS) alongside other open source security projects. Semgrep combines deterministic static analysis with advanced reachability analysis, interfile analysis, and AI-powered triage through Semgrep Multimodal, helping teams reduce noise and remediate issues faster.
Semgrep helps teams focus on the findings that matter by combining reachability analysis, AI-powered triage, and tailored remediation guidance. Developers receive actionable recommendations directly in their pull requests, while Semgrep Multimodal filters out noise and helps reduce time spent investigating false positives.
Semgrep is built for enterprise-scale codebases, including large monorepos. Advanced capabilities like reachability analysis, interfile analysis, and AI-assisted triage help security teams maintain high signal quality while scaling across large engineering organizations.
No. While Aikido is based on the open source Semgrep engine, Semgrep customers benefit from capabilities that are not part of the open source project, including Semgrep Pro Engine, advanced reachability analysis, interfile analysis, and Semgrep Multimodal. These capabilities help surface more exploitable vulnerabilities while reducing false positives.
Consolidation only delivers value if developers trust the results. Semgrep focuses on providing high-signal code security with advanced analysis, AI-assisted triage, and developer-first remediation workflows. Instead of overwhelming teams with alerts, Semgrep helps developers fix the issues that actually matter.
The overall value of a security platform depends on how effectively teams can identify and remediate real risks. Semgrep helps reduce investigation time through higher-signal findings, AI-assisted prioritization, and remediation guidance, allowing developers and AppSec teams to spend more time fixing vulnerabilities and less time triaging alerts.