Reduce false positives by
up to 98%
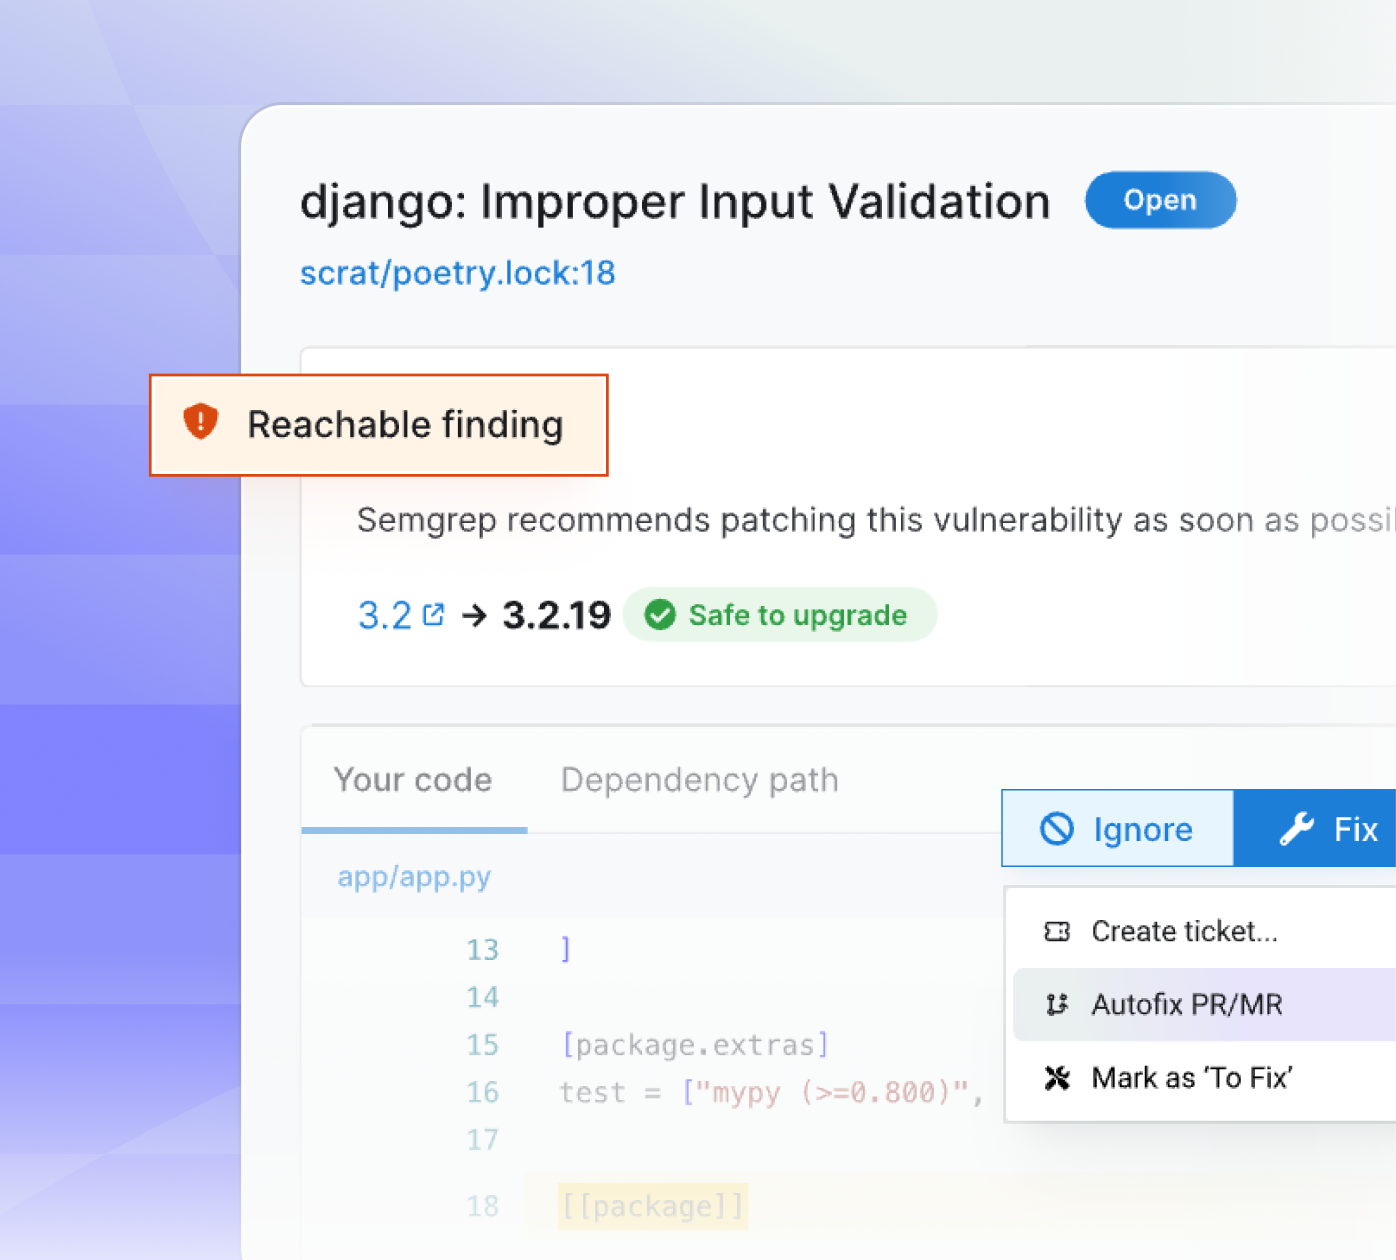
Semgrep's codebase-aware reachability analysis identifies the 2% of dependency vulnerabilities that are actually exploitable in your code, so your team stops chasing ghosts and focuses on real risk.
Upgrade without breaking things
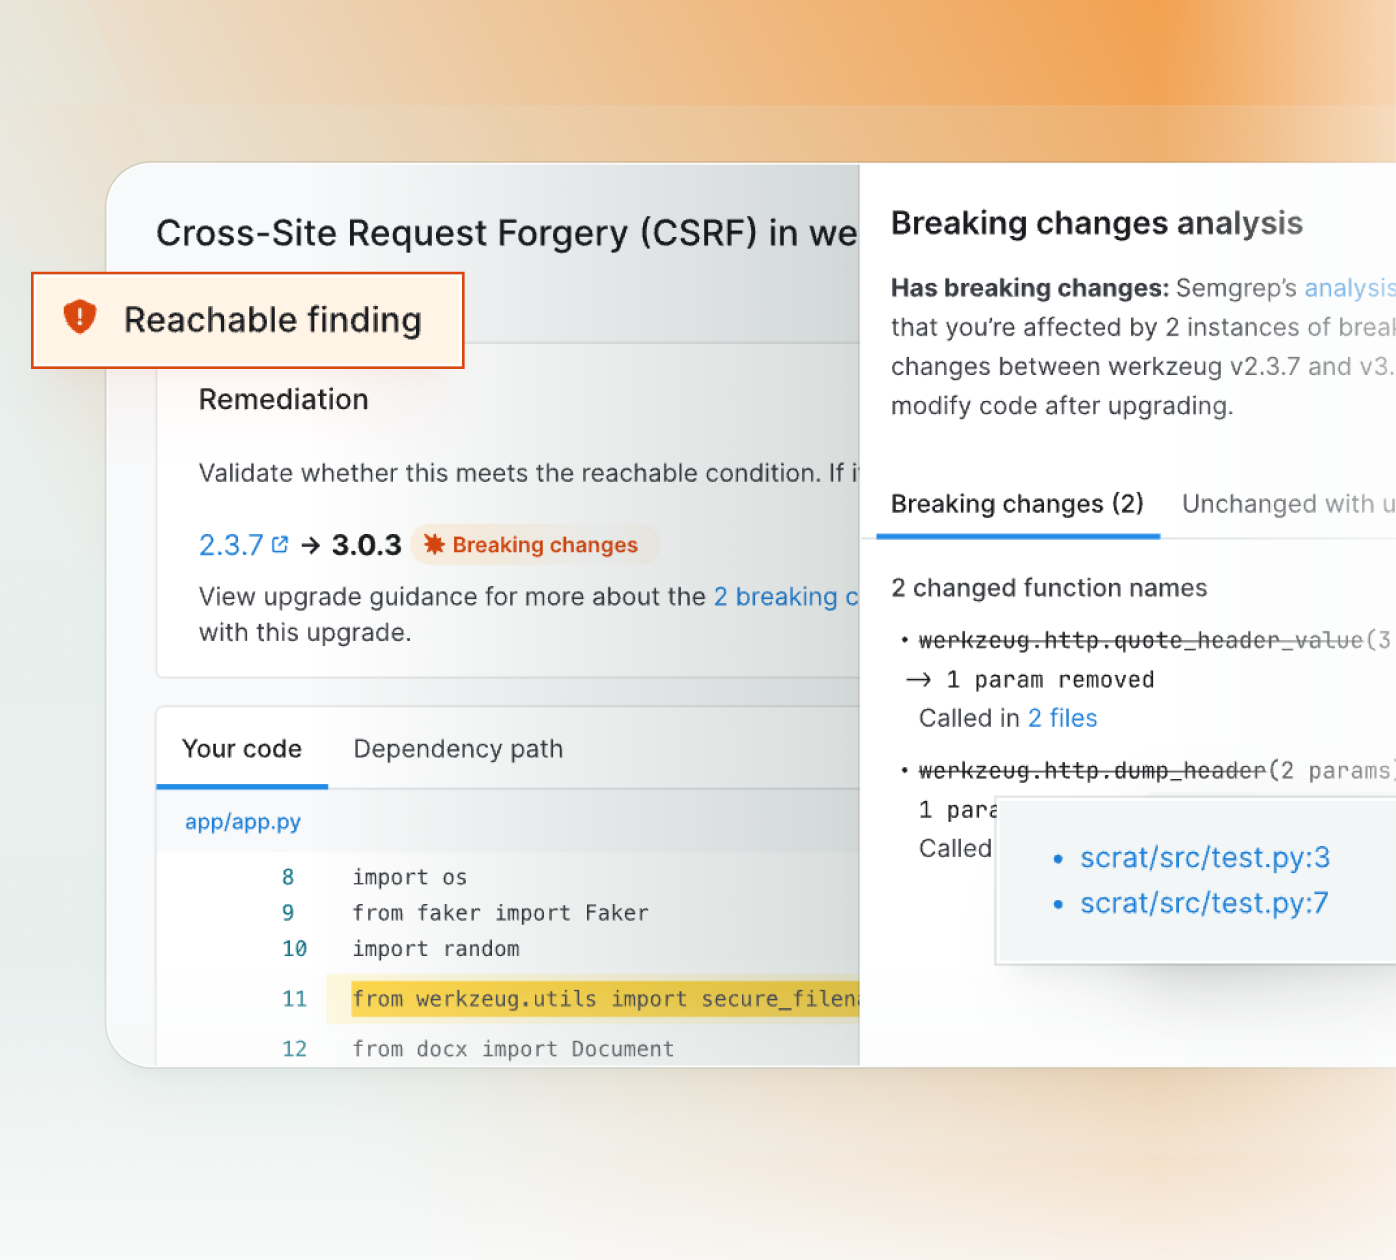
See the impact of every upgrade before it happens. Semgrep identifies breaking changes at the line level and generates fix PRs automatically, turning risky upgrades into routine ones.
Block malware before it reaches your codebase
See the impact of every upgrade before it happens. Semgrep identifies breaking changes at the line level and generates fix PRs automatically, turning risky upgrades into routine ones.
Focus on the right alerts,
at the right time.

See 98% fewer false positives
Focus on reachable alerts only
Automatically resolve code issues in minutes



LOVED BY LEADING ENGINEERING TEAMS

98% fewer false positives
Codebase-aware reachability filters out dependency vulnerabilities that can't actually be reached

12 languages supported
Get GA-level support for critical and high-severity dependency findings across 12 languages.

96% agree rate
After analyzing over 6 million security findings, Semgrep has a 96% agreement rate from users and security researchers

"Semgrep Supply Chain helped us be more productive by reducing the number of false positives."
Jessica Grider
Sr. DevSecOps Engineer, Policygenius
"Our engineers are excited we’ve got Semgrep Supply Chain. Managing vulnerabilities in NPM packages is chaos without any sense of reachability."

Rob Picard
Security Lead
"Nobody wants to be the security engineer who cried wolf, but doing the sophisticated analysis to find the real vulnerabilities takes lots of work. Use an expert tool like Semgrep Supply Chain to do it for you."
Roger Thornton
Former Founder & CTO of Fortify
“Semgrep Supply Chain has helped reduce the noise by 95%”
Khanh Le-Do
Security Software Engineer at Lyft
"Semgrep Supply Chain helped us be more productive by reducing the number of false positives."
Jessica Grider
Sr. DevSecOps Engineer, Policygenius
"Our engineers are excited we’ve got Semgrep Supply Chain. Managing vulnerabilities in NPM packages is chaos without any sense of reachability."
Rob Picard
Security Lead
"Nobody wants to be the security engineer who cried wolf, but doing the sophisticated analysis to find the real vulnerabilities takes lots of work. Use an expert tool like Semgrep Supply Chain to do it for you."
Roger Thornton
Former Founder & CTO of Fortify
“Semgrep Supply Chain has helped reduce the noise by 95%”
Khanh Le-Do
Security Software Engineer at Lyft
Semgrep Supply Chain is a software composition analysis (SCA) solution that uses codebase-aware reachability analysis to help teams prioritize the dependency vulnerabilities that matter most. It reduces noise, helps developers focus on real risk, and accelerates remediation with Autofix and AI-powered upgrade guidance.
A third-party evaluation by Doyensec compared Semgrep, Snyk, and Dependabot on their ability to identify which dependency vulnerabilities were actually reachable. Dependabot returned 97 false positives, Snyk returned 77, while Semgrep filtered all but two.
Semgrep provides visibility into the licenses used across your dependencies, lets you enforce license policies, block pull requests that violate your requirements, and search your codebase for any dependency and version.
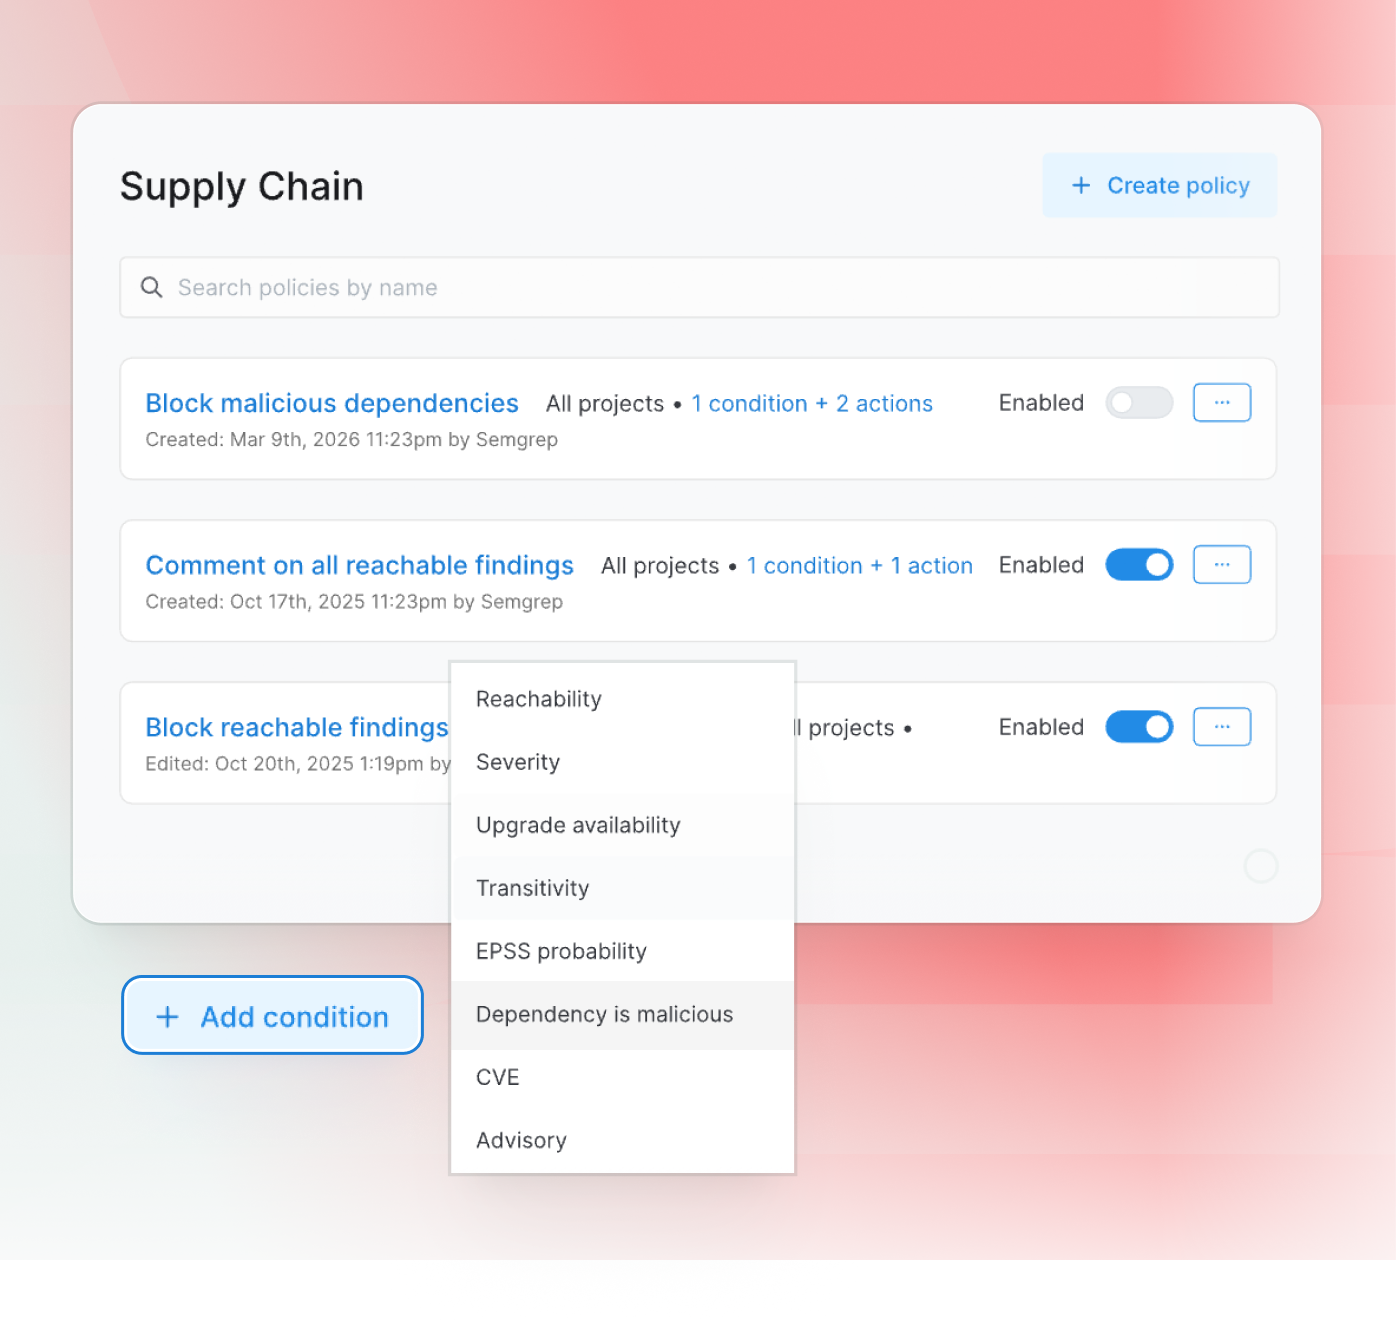
Semgrep automatically scans dependencies against a continuously updated database of confirmed threats. It detects malicious open-source packages, hallucinated package names, and typosquatting attempts before they ever install in your environment.
Yes. Semgrep's Autofix feature generates fix PRs for dependency vulnerabilities automatically. It also performs line-level breaking change detection before creating the PR, so developers know exactly what will be affected by an upgrade before it happens.


© 2026 Semgrep, Inc. Semgrep is a registered trademark of Semgrep, Inc.
Secure your supply chain with
the world’s most powerful detection engine
98% fewer false positives
Malicious packages blocked instantly
Automated fix guidance

How Semgrep protects
your supply chain
Reduce false positives by up to 98%
Semgrep's codebase-aware reachability analysis identifies the 2% of dependency vulnerabilities that are actually exploitable in your code, so your team stops chasing ghosts and focuses on real risk.
Upgrade without breaking things
See the impact of every upgrade before it happens. Semgrep identifies breaking changes at the line level and generates fix PRs automatically, turning risky upgrades into routine ones.
Block malware before it reaches your codebase
See the impact of every upgrade before it happens. Semgrep identifies breaking changes at the line level and generates fix PRs automatically, turning risky upgrades into routine ones.
Why security teams
love Semgrep
Semgrep Supply Chain scans every pull request to identify vulnerable and malicious dependencies as they're introduced.
Analyze your dependencies
1


Codebase-aware reachability analysis helps your team focus on dependencies that are actually reachable, reducing noise and unnecessary investigation.
Prioritize real risk
2


Generate Autofix PRs, detect breaking changes, and receive AI-powered upgrade guidance to resolve vulnerabilities without disrupting your application.
Remediate with confidence
3


We make triage easy as 1,2,3
Flexible security rules
Use enterprise-grade, configurable policies for finely-tuned security automation.

Find any dependency
Search your entire codebase for any dependency at any version, on-demand.

Stay compliant
SBOM generation with CycloneDX helps you track and prove everything that’s in your code.
All your licenses and dependencies. Total visibility.

Swamped in dependency alerts
No reachability context
Malicious packages slip through
Upgrades break unexpectedly
Slow, manual remediation
Without Semgrep

With Semgrep
Focus on exploitable risks
Detect malicious packages early
See what breaks before you upgrade
Fix dependency issues in minutes
Prevent license compliance issues
Get full visibility into every dependency in your codebase
See 98% fewer false positives